S&P 500 security disclosures show a step change, and the protection programs behind them are wider than a bodyguard

By Albina Bieci, Staff Writer
Aggregated proxy disclosures show personal security allocations climbing sharply year over year, while the assignments themselves now include residential assessments, stalking response and technical countermeasures.
NEW YORK
NEW YORK — Personal security allocations for chief executives and other named executive officers climbed sharply across the S&P 500 in the latest proxy season, according to the aggregated corporate governance disclosures reviewed by the Harvard Law School Forum on Corporate Governance, with the prevalence of comprehensive programs rising again year over year rather than drifting.
The disclosure trend has been building for several years, and this week's reporting confirms a step change rather than a slow line. The more consequential shift, however, is not in the amount of money disclosed. It is in what the money now buys.
The filing is a risk finding
A proxy statement is a legal document. When a compensation committee reports a personal security benefit, it is telling shareholders that the exposure is a business necessity rather than a perk, because the expense becomes defensible only if the risk to the company is defensible with it. A line item that grows year over year is a committee saying the assessment changed, not merely that the chief executive asked for more.
That assessment is rarely written down publicly. What is visible is the direction: more firms disclosing, larger figures at the firms already disclosing, and a broader definition of what counts as a security benefit. An item that ten years ago meant a car and a driver now appears in filings alongside residential systems, travel risk programs, communications review and threat monitoring.
What changed is the perimeter, not the philosophy
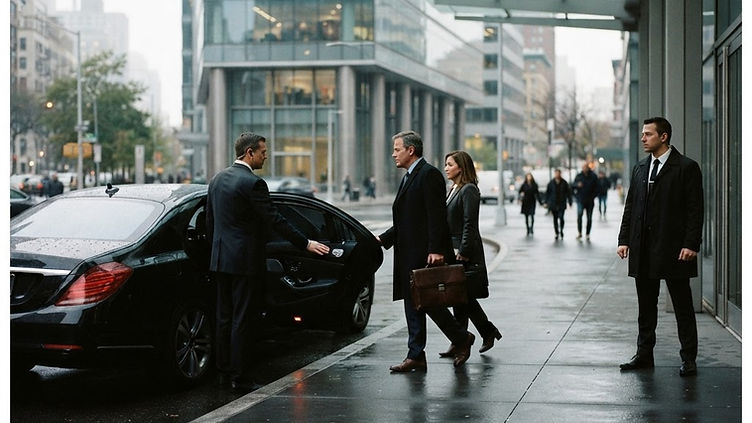
The classic protection detail is built around movement: a principal leaves a building, enters a vehicle, arrives somewhere, and the risk sits in the gap between those events. That model remains the core of the work and remains what most contracts describe.
The assignments that have expanded are the ones outside the transit window. Three stand out.
Residential exposure. An executive's home is now a public record with coordinates. Property filings, drone footage, family social media and commercial imagery databases have collapsed the effort required to locate and observe a residence. What used to be a periodic assessment has become a standing question about sightlines, gate response, camera coverage, household staff vetting and the behaviour of the street itself.
Stalking and fixation response. A meaningful share of protective work now begins with a person rather than a place: communications, arrivals, gifts, an account that keeps reappearing. That caseload requires documentation discipline, coordination with law enforcement and counsel, and the willingness to say when a threat has crossed from nuisance to pattern. It is also the category where companies most often start too late, after the principal has already normalised the contact.
Technical threat mitigation. Boardrooms, residences, vehicles and executive travel are all environments where the exposure may be invisible on arrival. A technical surveillance countermeasures survey, device review and communications hygiene program now sit inside the same protective scope as the officer at the door, and the boards paying for them are increasingly asking for documentation rather than assurances.
Why the disclosures lag the decision
The filing is written after the money is spent. The pattern in the data, year after year, is that programs expand in response to an event: a break-in, a credible threat, a public controversy, a family matter that reaches a journalist. The budget follows the incident, and the disclosure follows the budget.
That sequencing is expensive. A program assembled during an incident pays crisis rates, accepts whatever personnel are available, and inherits procedures written under pressure. A program assembled before one is cheaper, staffed properly and documented well enough to survive scrutiny, whether that scrutiny comes from a shareholder plaintiff, an insurer or a court.
The commercial argument for acting early is not abstract. Protection contracts that are scoped in calm conditions can specify assessment frequency, reporting format, escalation thresholds and the named person who receives a report. Contracts written during an incident specify coverage hours and little else.
The procurement problem
Most corporate security spending still flows through agreements written for a guard service, and a guard-service agreement cannot describe a program. The failures are predictable.
Who owns the residential assessment, and how often is it repeated? Which findings are documented, and who receives them? Is the threat caseload tracked in a system the company can produce, or in an officer's notebook? Are technical surveys scheduled, or ordered after something is found? Does the detail have written authority to escalate a principal's movement decision, or does it require a phone call to a general counsel who is asleep?
Each of those questions has a defensible answer. Few agreements contain one.
What the board should be asking
The disclosure line is the least useful place to start. The useful questions are about scope and evidence: what is covered, who assessed it, how often the assessment is repeated, what the reporting looks like, and what happens in the first hour of an incident that is not a medical emergency.
Corporate governance reviewers have made the same point in a different register. A security benefit that cannot be explained to shareholders is a liability, and one that can be explained but not evidenced is worse, because it invites the assumption that the company is buying reassurance rather than capability.
The family sits inside the perimeter
Protective programs are usually sold around one person and quietly relied upon to cover a household. The two are not the same assignment. A spouse's schedule, a child's school and activities, a household staff roster, a rideshare account, a birthday post that includes a street sign: each is a route to the principal that does not pass through the principal.
The disclosures do not capture this, because the benefit is reported for the named executive. The spending that actually addresses it appears under residential systems, household staffing or a broader security line, and it is the portion of a program most often trimmed when a budget is reviewed by someone reading coverage hours rather than exposure. Yet the cases that become public, and the ones that reach litigation, disproportionately begin with a family member, a residence or a household employee rather than with the executive at a lectern.
What the proxy line does not cover
Domestic protection programs are scoped to a jurisdiction and a routine. The same executive's exposure changes when travel leaves the country: medical standards, police response, hospital access, firearms authority, data protection and the legal status of a protective agent all differ, and a detail trained in one country cannot be assumed to work in another. Multinational firms increasingly expect a vetted provider at the destination rather than an unfamiliar local hire arranged by a hotel, and they expect the itinerary to include a medical plan and a communications plan before the flight.
Those costs are rarely disclosed as security. They appear as travel, as professional fees, or not at all. Their absence from a proxy statement is not evidence that the exposure is managed.
The cost of doing it badly is visible too
The same disclosure regime that rewards a well-run program exposes a badly run one. A security benefit that appears in a filing but cannot be matched to a documented assessment invites the conclusion that the company is paying for reassurance. That conclusion is expensive when it is drawn in a deposition, and it is expensive in insurance terms as well, because underwriters increasingly ask for the assessment record before they price a risk that involves a publicly identified principal.
The practical consequence is documentation discipline. Findings written down, corrections closed, drills logged, and a named owner for every open item. None of that is glamorous. All of it is what distinguishes a program from a purchase.
What a program should be able to show
The question a board, an insurer or a plaintiff's lawyer will ask is not how much was spent. It is what the spending produced. A functioning program can produce four things without a scramble: the date and author of the last residential assessment, a threat log with entries and dispositions, a record of the last two drills or exercises, and the escalation path with names and numbers attached to it.
A program that cannot produce those is a coverage arrangement. Coverage is useful, and it is not the same as capability. The filings reviewed this week suggest that corporate America has accepted the expense. Whether it has bought the evidence is a separate question, and one that will be answered under pressure rather than in a proxy statement.
Where the market is going
USPA's executive protection practice has moved in the same direction as the filings. Engagements now routinely combine a protective detail with residential and estate assessment work, corporate risk intelligence that maps exposure before a trip or a public appearance, and technical review of the environments a principal actually uses.
The company publishes its own reading of the disclosure trend, including an earlier analysis of proxy statements and personal security benefits across the S&P 500, and takes inquiries through the contact desk.
The finding this week is straightforward. Corporate America has decided that protecting its leadership is a recurring operating expense rather than a discretionary one. The next question, and the one the filings cannot answer, is whether the programs being paid for are built to report what they find.
Services in New York, NY
Sources
About the reporter
Staff Writer
Staff writer for the USPA Nationwide Security newsroom. Receives newsroom tips, corrections and editorial inquiries.
Author biography and credentialsMore from The Watchline

Executive Protection
A WNBA guard hired protection around the clock, and the case file explains why
An Indiana Fever guard has put a continuous close protection detail in place after sustained stalking, with more than twenty individuals now under federal scrutiny in connection with the case.
· Albina Bieci
Executive Protection
An unsealed entry, a home invasion and the hardening that followed
Court records confirm the intruder who entered the Clinton Township residence of Marshall Mathers came through an unsealed opening, a failure that led to a hardened estate posture built around denial of close-quarters access.
· Albina Bieci

Executive Protection
A private detail stopped a repeat intruder at the gate, and the arrest came after
Security agents detained a 25-year-old man with a documented multi-state history at the Calabasas estate before he could breach the inner perimeter, and sheriff's deputies arrested him on stalking and trespass charges.
· Albina Bieci
